
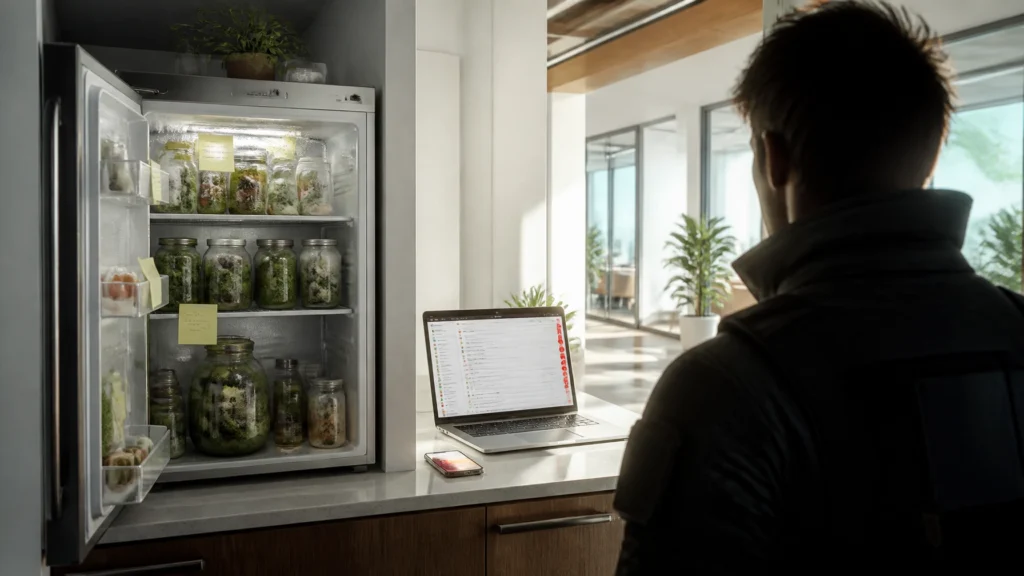
At FindASpy headquarters, the office mini-fridge has entered its experimental phase.
Tracer opens the door before his espresso finishes brewing and discovers three labeled jars, one suspiciously swollen lunch container, and a colony of something that appears to have opinions. A sticky note reads: “Do not disturb. Week 4.”
The fridge hums.
The jar bubbles.
Then Tracer’s laptop begins chiming.
One email arrives. Then another. Then dozens.
Subscription confirmations. Password-reset notices. Mailing-list welcomes. Account-verification messages. The inbox fills so quickly that the unread counter looks less like a number and more like a cry for help.
Before Tracer can investigate the fridge or the inbox, his phone rings.
“Hello, this is your IT support department,” the caller says. “We noticed the email emergency. We are already working to fix it.”
The caller knows exactly what is happening. He describes the flood. He uses the right technical phrases. He sounds calm, helpful, and prepared.
Then he says, “Please open Quick Assist. I will give you a code.”
That is the moment the scam begins.
This attack is called email bombing. Criminals use automated forms and legitimate websites to subscribe a target’s email address to thousands of newsletters, confirmation lists, and account notifications.
The individual messages are often real. That is what makes the attack effective.
The victim sees a wall of ordinary emails and assumes the problem is random spam. Important messages disappear inside the flood. A bank alert, password-reset warning, fraud notification, or security notice sits unnoticed among hundreds of harmless confirmations.
The inbox flood creates confusion. It also creates a believable reason for the next step.
Minutes later, the criminal calls or sends a Microsoft Teams message while pretending to be internal IT, a helpdesk worker, or Microsoft support.
The fake technician says:
The caller sounds credible because he accurately describes the chaos he created.
That is the con.
The flood is the setup.
The IT call is the deception.
The remote-access tool is the doorway.
Once the victim approves a remote session, the criminal has interactive control of the computer. The attacker sees the screen, moves the mouse, opens files, launches programs, and searches for credentials. The criminal then steals information, installs malware, creates persistence, or moves toward ransomware.
Security researchers have linked this email-bombing and fake-helpdesk pattern to Storm-1811 and Black Basta-associated campaigns. CISA has also documented attackers using phone calls, Microsoft Teams, AnyDesk, and Microsoft Quick Assist to obtain initial access. Current reporting shows the technique continuing to evolve against businesses, healthcare organizations, executives, and employees working from home.

This scam does not depend on a victim being careless. It targets a normal human response: when technology breaks, people look for help.
Seniors and retirees often manage years of digital accounts. Their inboxes contain medical portals, tax services, airline accounts, family communications, banking alerts, and shopping receipts. An email flood hides the message that matters most.
Working families face a different pressure. A parent working remotely sees thousands of messages arrive while trying to meet a deadline. A small-business owner worries about losing access to customer records. An employee fears that ignoring “IT” will cause a major outage.
The criminal uses that pressure.
The caller ID looks familiar. The Teams profile displays “IT Support.” The caller knows the victim’s name, employer, email address, or department. The story sounds reasonable because the victim is genuinely experiencing an inbox emergency.
The criminal does not need to sound threatening. He sounds useful.
That is why this scam reaches beyond large corporations. A home office, family laptop, small law firm, medical practice, or local business is enough. One remote-access approval gives the attacker a foothold.
The clearest warning is the timing:
Real IT does not call unsolicited to install software. No one who works for your company asks for remote access out of the blue. A legitimate helpdesk follows a documented process, uses a known ticket, and provides a verifiable contact path.
Microsoft Teams is a legitimate business tool. Quick Assist is a legitimate support feature. AnyDesk and TeamViewer are legitimate remote-access products. Their legitimacy does not make an unsolicited support session safe.
The question is not, “Is this software real?”
The question is, “Who is asking me to use it, and how did I independently verify that person?”
Do not open Quick Assist. Do not approve a Teams screen-sharing request. Do not install AnyDesk, TeamViewer, ScreenConnect, or another remote-management tool because an unexpected caller instructs you to do so.
A remote-access code is not a harmless troubleshooting step. It gives another person a path into your device.
Tell the caller, “I do not accept unsolicited remote support.” Then end the call.
Use the phone number stored in your company directory, employee handbook, official intranet, or existing helpdesk portal. Do not use the number provided by the caller. Do not reply to the Teams account that contacted you.
If you work for a small business, create a written IT-support policy before an emergency happens. Identify who provides support, which tools are approved, and how employees verify an unexpected request.
For family devices, choose a trusted relative or local professional and save that person’s number in advance.
The one-time code, access code, or session number is the criminal’s bridge to your computer. Do not read it aloud. Do not type it into a support window. Do not click a download link sent by the caller.
If a legitimate technician needs access, initiate the conversation through a verified channel and follow your organization’s approved process. Do not let urgency replace verification.
Do not spend an hour deleting messages one by one. First, look for important notices from your bank, email provider, payroll system, cloud storage, and password manager.
Use your email provider’s filtering and reporting tools. Create rules that route obvious subscription confirmations into a review folder. Ask your IT administrator to monitor sudden spikes in newsletter and account-confirmation traffic.
The flood is not only an annoyance. It is an indicator that someone is trying to distract you.
If you approved remote access, end the session immediately. Disconnect the computer from Wi-Fi and unplug the network cable. Use a different, trusted device to contact your real IT team, email provider, bank, and other critical services.
Change passwords from the trusted device. Prioritize email, banking, cloud storage, payroll, and administrator accounts. Revoke active sessions, review multifactor-authentication methods, and check for unfamiliar recovery addresses or newly created users.
Do not assume that uninstalling the remote-access program removes the compromise. The attacker installs additional tools and changes settings after access begins.
For a business, preserve logs and contact qualified incident-response professionals before wiping the device. For a personal device, a professional breach assessment is appropriate when the caller opened files, accessed financial information, installed software, or requested passwords.
FindASpy provides discreet digital-security consultations and spyware or breach-removal services. You can review the available services, learn more about the team, or call Patricia at 321-342-0040. If the incident involves business ransomware, also notify your organization’s insurer, legal counsel, and an established ransomware-response provider.

Criminals use familiar platforms because familiarity lowers resistance.
A Teams message feels more trustworthy than a random email. Quick Assist feels safer because it is built into Windows. A caller who knows the exact problem appears informed.
But trusted technology does not verify the person using it.
The same principle applies to your wider privacy network. Review the security tools and counter-surveillance equipment available through the FindASpy product catalog, but remember that no device replaces careful verification, strong account security, and a clear incident plan.
Awareness is the first layer. Knowledge is the second. Protection is what you build from both.
This week, Tracer’s Pick is the known-number rule:
If someone contacts you unexpectedly about a security problem, stop the conversation and call the real organization through a number you already trust.
It is a small habit with a large protective value. Keep sharing these Coffee Time lessons with your household and team. FindASpy occasionally offers reader-focused giveaways and protective picks, so stay connected for future selections.
This article is for general educational and awareness purposes. It is not legal advice, financial advice, or a substitute for professional cybersecurity incident response. FindASpy does not claim that every email flood or support contact is connected to Storm-1811 or Black Basta. Remote-access software has legitimate uses, but it must be controlled through a verified support process. If you suspect a compromise, preserve relevant evidence and contact your organization’s IT, legal, insurance, law-enforcement, or qualified incident-response professionals as appropriate.
Have you or someone you know received a sudden flood of emails followed by an unexpected “IT support” call or Teams message?
Which State are you reading from?
Do you have a written support number saved for your workplace, family, or small business? What is the first thing you would check if your inbox suddenly filled with thousands of messages?
Tracer reads all posts, and your experience could help another member of our community recognize the setup before granting access.
Have you found a hidden camera, tracker, recorder, or other unexpected gadget? Upload it for the community by clicking here.
A flood of spam is not always the attack. Sometimes it is the distraction that makes the fake technician believable.
Ask your family or team one question today:
“If someone claiming to be IT calls unexpectedly, which trusted number will we use to verify them?”
Write the answer down before an emergency creates pressure.
Tomorrow is Coffee & Conversation: a recap of the week’s privacy and security lessons, with no new scam story. Bring your coffee, compare notes, and stay one step ahead.
Your vote helps determine FindASpy Insider’s Readers’ Top Picks. One rating is allowed per reader for each article.
Today’s Coffee Conversation
Tracer shares cybersecurity stories, scam alerts, privacy tips, and investigative insights. Pull up a chair, share your experience, and help shape tomorrow’s discussion.