
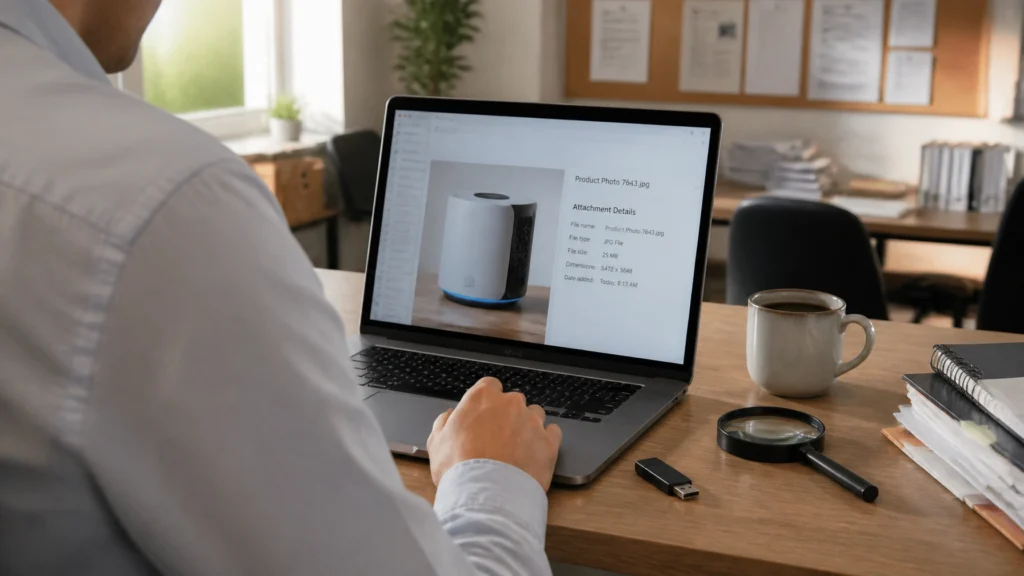
Tracer’s pour-over coffee was halfway through its morning drip when the label printer at FindASpy HQ produced a warning nobody had programmed into it:
DO NOT TRUST THE JPEG.
Tracer stared at the label.
“I trust JPEGs,” he said. “I just don’t trust printers with opinions.”
A small business owner had arrived with a laptop and a supplier email. The message looked routine. It included a product photograph and a note telling the recipient to “open the updated price list.”
The photo opened normally. It showed a familiar product on a white background. There was no frightening warning, no obvious pop-up, and no strange file extension.
Several days later, the company accountant noticed unusual network activity. The office computer was contacting an unfamiliar internet address after business hours. The laptop also became slower whenever the accounting software was open.
The owner brought the computer to Tracer.
The first thing Tracer noticed was the file size.
The photograph looked like a small product image. It was not a high-resolution catalog image. It was not a video. It was not a design file.
It was 25 megabytes.
“That is a very large suitcase for a picture this small,” Tracer said.
He examined the file structure and found data after the JPEG’s normal ending marker. The image displayed because most image viewers stopped reading at the picture’s true end. The extra bytes remained behind the picture.
Those bytes were not ordinary image information. They contained an encoded executable payload designed to be extracted by another script or program and then connect outward.
That distinction matters. A JPEG does not normally run a program simply because someone views it. A hidden payload needs a loader, a malicious script, a vulnerable application, or another execution path. In this case, the evidence indicated that a later process had accessed the file, extracted its contents, and initiated the suspicious connection.
The photograph was only the disguise.

Steganography means hiding information inside something ordinary so the hidden information is not obvious.
A person can hide a message inside an image, video, audio recording, document, or even a block of text. The carrier still looks normal to the person viewing it.
In a harmless use, someone might hide a private message inside a photograph.
In a criminal use, an attacker might hide:
The hidden material is often called the payload. That simply means the data the attacker wants delivered.
Digital images are built from tiny color values. Each pixel contains information about its red, green, and blue components.
One technique is called least significant bit encoding, or LSB encoding. The least significant bit is the smallest part of a number. Changing it makes such a tiny adjustment to a pixel’s color that the human eye usually cannot see the difference.
An attacker can use those tiny changes to represent hidden data. The image still looks like an ordinary photograph, but a special program knows how to read the altered bits and reconstruct the hidden message or code.
Another method is more straightforward.
A JPEG, PNG, or other image format has a point that marks the end of the actual picture. Most image software reads the image until that point and displays it.
An attacker can append extra data after that marker. The picture still opens because the viewer ignores what follows. A separate script or loader then reads past the image’s ending, finds the hidden data, decodes it, and passes it to another process.
This is what made the supplier’s image so concerning. It had a valid picture at the beginning and suspicious material after the picture ended.
Images also contain metadata, which is information about the file rather than the visible photograph.
Metadata may include:
Some image formats allow long text fields. Those fields can carry instructions, encoded data, or scripts. A normal viewer may never show that content.
A real MP4 video can contain hidden material in several places:
A video that plays normally is not automatically safe. The same principle applies: the hidden material usually requires another program, script, exploit, or malicious player component to extract and use it.
Businesses use email filters to block obvious threats. Those systems look for executable files, suspicious scripts, malicious archives, and known harmful patterns.
Pictures and videos receive different treatment because companies exchange them constantly. A product photograph, invoice logo, shipping image, or training video does not look dangerous to a basic filter.
That trust is the opening.
Threat actors have used image files to deliver remote-access trojans, information stealers, ransomware components, and other malware. The MITRE ATT&CK knowledge base documents multiple groups and tools that extract malicious code from photos and PNG files. Security researchers have also reported campaigns in which an image was downloaded from a legitimate file-hosting or image-hosting service and used as the carrier for a hidden loader.
In one documented campaign, a JavaScript dropper retrieved an image and extracted a .NET loader from it. That loader then helped deliver a remote-access trojan. A remote-access trojan, or RAT, is malware that gives an attacker the ability to control or monitor a computer.
Other campaigns have hidden PowerShell commands, executable files, or encrypted payloads inside images. Supply-chain attacks have also demonstrated how ordinary-looking media files can be used as containers for malicious content.
The picture is not necessarily the entire attack. It is often the quiet delivery truck.

File size is not proof of malware. A high-quality photograph may be large, especially if it came directly from a modern smartphone or professional camera.
Still, size is a useful warning sign.
As a general guide:
If someone sends you an ordinary-looking logo or small product photo that is 15 MB, 25 MB, or larger, stop and question it. A small image that is fifty times larger than expected deserves a second look before you open it or forward it.
Also question:
A large file is not automatically malicious. It is a clue, not a conviction.
On a computer, right-click the file and select Properties on Windows or Get Info on macOS.
On a phone, review the attachment or download details before opening it. If a small picture is measured in tens of megabytes, do not open it casually.
Do not reply to the email and ask whether it is legitimate. If the sender’s account is compromised, the attacker may answer you.
Call the supplier using a phone number already saved in your records. Use a separate invoice, contract, or official website. Ask whether the file was actually sent.
An instruction such as “open the image, then run this tool to see the hidden price list” is itself a major warning sign.
Do not run PowerShell, JavaScript, command files, installers, or unknown utilities because an email tells you to do so.
Update your operating system, browser, email application, and image and video viewers. Updates repair known vulnerabilities that attackers may use against specially crafted files.
A sandbox is an isolated environment that opens a file away from your normal computer. Business email systems and security software with sandbox scanning provide an additional layer of protection.
They are not perfect, but they are stronger than relying on the file extension or thumbnail alone.
If a picture causes a viewer to crash, the computer becomes unusually slow, a command window flashes, or the device asks permission to launch another program, close the file.
Disconnect from the network if practical. Do not continue experimenting on the computer. Have the device examined by a qualified professional.
Businesses should restrict programs from launching out of Downloads and temporary folders. Security teams should also monitor for image files being accessed by scripts, PowerShell, Python, or command-line tools.
Train employees to question oversized attachments. That simple habit prevents many avoidable incidents.

Do not panic, and do not assume that viewing a picture proves infection.
Write down:
If the computer is used for banking, payroll, legal work, medical information, or business credentials, avoid using it for sensitive activity until it has been checked.
FindASpy’s Guardian Angel Spyware and Breach Removal service reviews devices and networks for spyware, unauthorized access, and related compromise indicators. When contacting the team, mention the Tracer2026 discount.
A file can look harmless and still carry hidden information.
A photograph can contain extra data in its pixels, metadata, or trailing bytes. A video can carry hidden material in its frames, tracks, or file structure. The carrier may display normally because the ordinary viewer is only reading the visible portion.
The safest approach is not to fear every image. It is to verify unexpected files, question unusual sizes, refuse suspicious instructions, and investigate abnormal behavior quickly.
Awareness gives you time. Knowledge gives you options. Protection keeps the hidden payload from becoming an active breach.
Before your next cup of coffee, complete these three actions:
Have you ever received an ordinary-looking photo, logo, or video that was strangely large? Did anyone ask you to run a tool, enable content, or use a password to view it?
Tell us what happened, and share which State you are writing from. What file type makes you most cautious: JPEG, PNG, MP4, PDF, or something else?
Tracer reads all posts.
If you have found a hidden gadget or suspicious device of your own, upload it to our Community Finds and share the lesson with the community.
This article is for general education and awareness. File size alone does not prove that a file contains steganography or malware. Do not attempt to extract, execute, or test suspicious payloads on a personal or business computer. For suspected compromise, preserve relevant information, disconnect the affected device when appropriate, and consult a qualified cybersecurity or digital-forensics professional.
Sterling Reed “Tracer” is associated with FindASpy.com, a privacy and security organization providing discreet consultations, device protection, surveillance detection, and spyware and breach-removal support.
In the next Coffee Time with Tracer, we will examine the small signs that reveal when a familiar account has been quietly accessed from an unfamiliar device: and the steps that help you take back control.
Your vote helps determine FindASpy Insider’s Readers’ Top Picks. One rating is allowed per reader for each article.
One Response
Great article
Today’s Coffee Conversation
Tracer shares cybersecurity stories, scam alerts, privacy tips, and investigative insights. Pull up a chair, share your experience, and help shape tomorrow’s discussion.